


“Day by day backups” is helpful plan-table language solely when the supplier additionally states how lengthy copies stay accessible and the way restoration works. “Firewall safety” wants a named layer plus a response coverage for blocked site visitors.
Safe website hosting begins with reliable platform controls. It additionally provides a workable restoration route for the shopper.
Handbook malware cleanup can moderately value extra as a result of a specialist should examine the compromised website. Remediation then fixes the exploited weak spot. Superior web-application filtering may additionally value extra for a higher-risk website. Earlier than buy, the bottom plan ought to describe its computerized response. It ought to inform the shopper which restoration step stays their accountability.

Included Protections to Confirm Earlier than Buy
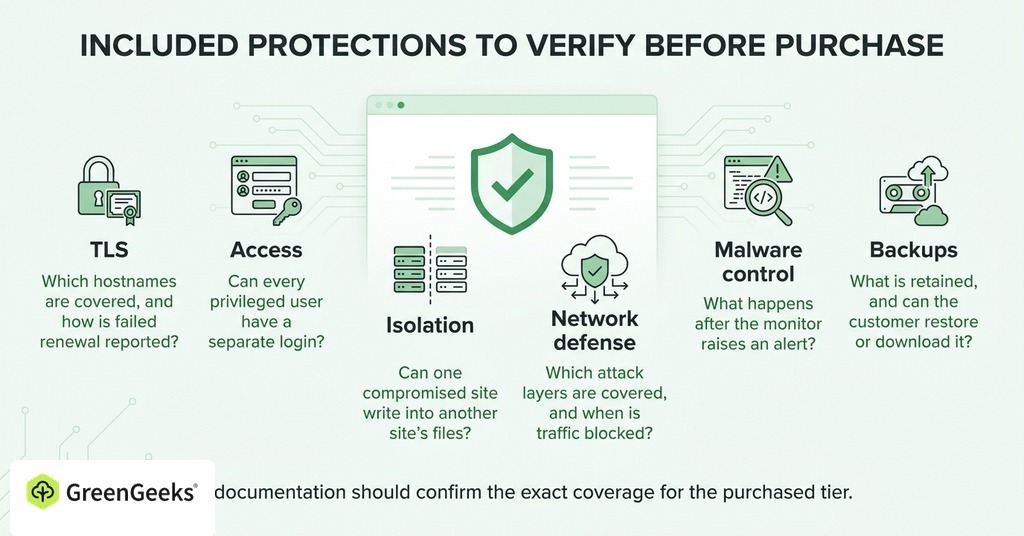
A reputable managed shared-hosting plan names how every safety works and what occurs when it fails.
| Safety | Included baseline | Implementation query |
| TLS | Computerized certificates issuance and renewal | Which hostnames are lined, and the way is failed renewal reported? |
| Entry | Multi-factor authentication with encrypted file switch | Can each privileged consumer have a separate login? |
| Isolation | Boundaries between clients and unrelated websites | Can one compromised website write into one other website’s information? |
| Community protection | At all times-on community filtering and fundamental DDoS mitigation | Which assault layers are lined, and when is site visitors blocked? |
| Malware management | Fundamental monitoring with an outlined alert route | What occurs after the monitor raises an alert? |
| Backups | Automated copies saved aside from the stay website | What’s retained, and might the shopper restore or obtain it? |
| Platform care | Supported runtimes and supplier patching | Which software program layers stay the shopper’s obligation? |
| Incident entry | A safety contact accessible in any respect hours | What data is provided throughout an incident? |
Suppliers can function these controls persistently throughout managed infrastructure. Plan documentation ought to affirm the precise protection for the bought tier.
Internet hosting Safety Duty
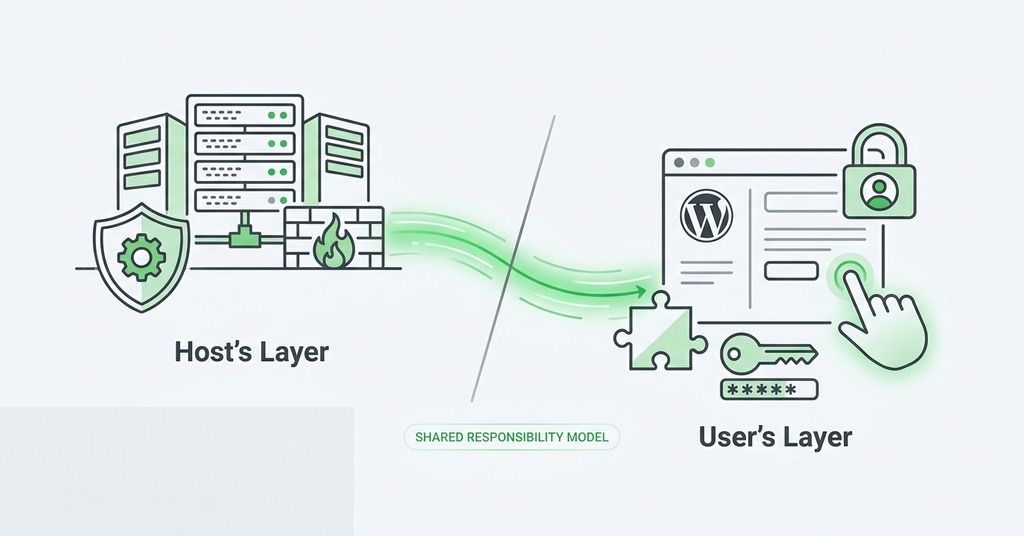
Internet hosting safety follows a shared-responsibility mannequin. On shared internet hosting, suppliers usually preserve the bodily system and the managed server layer. They need to additionally patch the management airplane and preserve separation between buyer accounts.
WordPress website house owners stay accountable for administrator identities and software knowledge. Plugins and themes additionally stay with the proprietor except the plan explicitly manages them. Customized code all the time wants a named maintainer.
The quantity of administration modifications the accountability boundary for every software program layer. An computerized WordPress core replace is a selected service. Plugin and theme protection requires an specific plan time period. Ask the supplier to call accountability for the working system and PHP runtime. Then receive the identical reply for the content material administration system and its extensions.
Migration to a brand new host can carry a compromised website’s contaminated information and stolen credentials. The trigger have to be corrected, and the alternative atmosphere wants new secrets and techniques earlier than restored content material is trusted.
How Every Included Safety Works
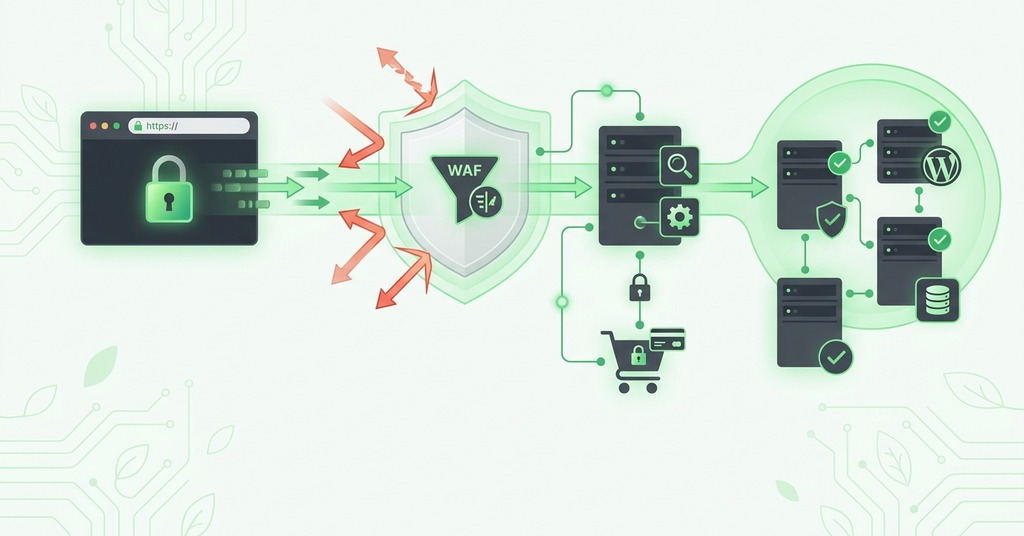
The most effective pre-sales questions describe a believable incident. A exact reply reveals greater than one other row of safety phrases.
Account entry and website isolation
Suppose a workers administrator leaves on Friday. Revoke that particular person’s particular person control-panel id and SFTP or SSH id instantly. The alternative administrator ought to enroll a brand new multi-factor methodology below a separate id. Unencrypted FTP mustn’t carry an administrative session. A retained file-access log then preserves attribution for exercise earlier than departure, which shared credentials would erase.
Isolation deserves consideration on shared internet hosting as a result of a number of clients use widespread infrastructure. The supplier ought to forestall one buyer account from studying or writing one other buyer’s information. A plan label reminiscent of “safe shared internet hosting” doesn’t describe that boundary.
Isolation inside one buyer account might be weaker. Inserting many unrelated websites below one writable id could let one compromised set up have an effect on the others. Ask if remoted website containers or accounts can be found, then use distinct credentials for websites with completely different house owners.
Community firewall and DDoS protection
A community firewall filters connections on the infrastructure boundary. An internet software firewall inspects HTTP requests for patterns related to assaults on the applying. The phrase “firewall” alone doesn’t set up {that a} managed WAF or a specific ruleset is included.
Fundamental community DDoS mitigation ought to function constantly on a reputable platform. Ask which assault varieties are lined and if mitigation begins mechanically. The supplier also needs to clarify any capability restrict or null-routing coverage. Utility-layer floods could require a CDN or WAF service past the entry plan.
Malware monitoring and response
Malware scanning can determine suspicious information or conduct. An alert wants an outlined recipient and a response path. Ask how rapidly the shopper is notified and if the supplier mechanically quarantines information.
Cleanup is an extra service. It might require inspection of information and the database, adopted by restore of the exploited weak spot. Blacklist appeals or incident forensics add extra labor. A base plan can moderately cost for this work when detection and the cleanup boundary had been disclosed earlier than buy.
Backups and restoration
Backups restore information and databases after compromise or unintended change. Day by day frequency is a sensible ground for a low-activity brochure website, whereas a busy retailer may have restoration factors inside the day.
With 7 every day restore factors, a compromise found after 2 weeks has no clear every day copy. Longer retention or an earlier impartial copy preserves a restoration level exterior that bounded window.
Backup protection issues as a lot as frequency throughout a WordPress restoration. The restoration wants the database and uploaded media. It additionally wants the related configuration information that outline the set up. Verify {that a} full copy might be downloaded with out ready for help.
GreenGeeks lists every day backups on present WordPress plans. On-demand backup and restore can be found solely on choose plans. Plan descriptions should determine who can provoke restoration and provides the conventional support-assisted restoration time.
Check a restore after setup and after a significant platform change. Use staging or one other disposable location. Open the restored website and confirm a consultant type. File the process so the following administrator can repeat it throughout an incident.
Maintain an impartial copy exterior the internet hosting account. A billing lockout or supplier failure could make an inside backup inaccessible on the time it’s wanted.
Supported software program and safety contact
Present server software program and a migration path away from an expiring runtime belong within the internet hosting baseline. For WordPress, that features a present PHP department and supported database software program. Promoting malware monitoring whereas leaving functions on an end-of-life runtime is an avoidable battle.
Ask which server layers obtain computerized safety patches. File the shopper’s replace duties in their very own part of the service file. If the plan consists of WordPress core updates, affirm how failed updates are reported and if rollback is out there.
Internet hosting suppliers ought to publish a safety contact and an incident-notification course of. Throughout a supplier incident, the shopper wants the affected service and related time window. It additionally wants sensible containment directions. Pressing safety circumstances require an outlined escalation route from any basic help inbox.
Safety work that may moderately value extra
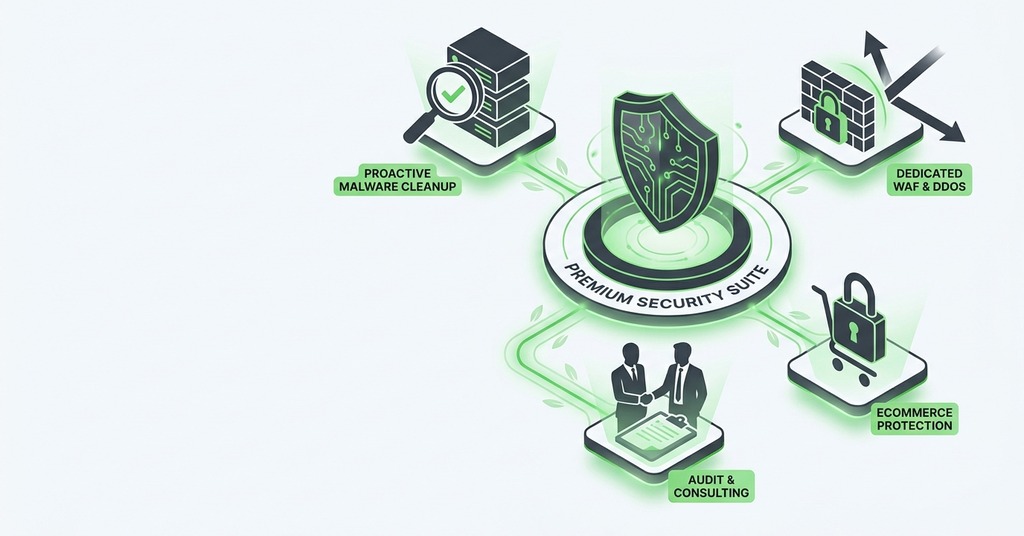
Paid safety is justified when the service assigns human work to an outlined incident. When a specialist removes malware by hand, the charge pays for incident labor. Vulnerability remediation can comply with after cleanup identifies the entry level. Superior WAF administration may additionally be an add-on. Excessive-capacity application-layer DDoS response belongs in a named service tier. Bot administration might be priced individually when the positioning attracts automated abuse.
Lengthy retention consumes storage. Extra frequent restoration factors add working work for the supplier. Managed catastrophe restoration can embody restoration workout routines tied to a restoration goal. Compliance help requires specialist information of the related regulatory management framework. Incident forensics provides investigation after a compromise.
Utility upkeep is one other cheap paid boundary when the supplier accepts replace accountability. A supplier could check plugin updates earlier than launch. Compatibility restore requires specific scope for every lined part within the contract. The contract ought to determine each lined software. It also needs to clarify the dealing with of an pressing safety replace. A broad “safety package deal” with out these deliverables merely provides one other unexplained label.
Incident Response as a Shopping for Check
Select the least costly plan that provides a whole written reply to a believable incident. Earlier than shopping for, ask what detects a weak plugin exploit in a single day and who contacts the shopper. The supplier ought to identify any computerized containment and determine the newest clear restoration level.
A second reply should assign the cleanup work and state its value. If the gross sales staff can’t identify the accountable get together earlier than buy, the enterprise can have the identical uncertainty throughout the incident.
