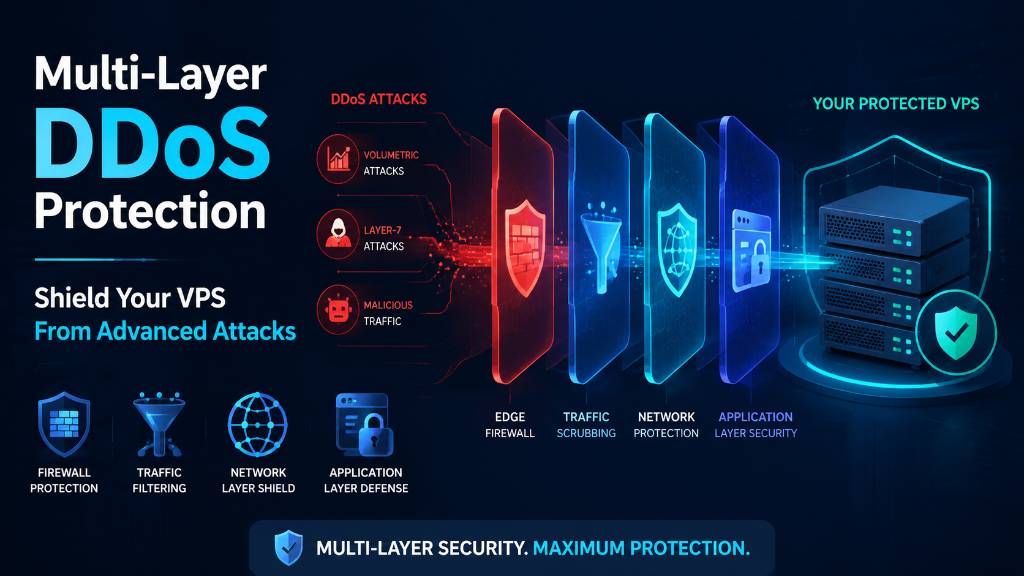


🛡️ VPS DDoS Safety: Government Abstract
- Multi-Layer Protection: A strong VPS DDoS Safety structure entails neutralizing Layer 3 (Community), Layer 4 (Transport), and Layer 7 (Software) assaults utilizing a mixture of edge filtering and native firewall guidelines.
- Volumetric vs. Software Assaults: Whereas huge UDP/SYN floods try to saturate your bandwidth, stealthy Layer 7 assaults (like HTTP floods or Slowloris) goal to exhaust your net server’s connection limits.
- Iptables & Fail2Ban: Using kernel-level
iptablesfee limiting and automatic IP banning by way of Fail2Ban offers an important final line of protection straight in your server. - Infrastructure {Hardware}: Deploying on a premium community spine, like a managed devoted server, offers the required bandwidth overhead to soak up preliminary assault spikes earlier than mitigation guidelines kick in.
1. Introduction: Understanding the DDoS Menace Panorama
Distributed Denial of Service (DDoS) assaults are designed to overwhelm a server’s assets, rendering web sites and functions inaccessible. As botnets grow to be cheaper and extra subtle, commonplace unmanaged servers are more and more susceptible to sudden, devastating outages.
An efficient VPS DDoS Safety technique have to be multi-layered. No single software can cease all assault vectors. Directors should differentiate between volumetric assaults (which clog the community pipe) and application-layer assaults (which exhaust server reminiscence and CPU). By combining edge filtering with localized OS-level hardening, you may architect a extremely resilient internet hosting setting.
2. Mitigating Layer 3 and Layer 4 Assaults (SYN/UDP Floods)
Layer 3 and Layer 4 assaults, reminiscent of UDP amplification floods and TCP SYN floods, are purely volumetric. They don’t care about your net server; they merely need to fill your community interface card (NIC) past its capability or exhaust the TCP connection state desk.
Step one in mitigation is SYN Cookies. When an attacker sends hundreds of SYN packets (initiating a connection) however by no means completes the handshake, the server’s backlog fills up. Enabling SYN Cookies permits the Linux kernel to deal with these requests statelessly.
3. Neutralizing Layer 7 Assaults (HTTP Floods & Slowloris)
Layer 7 assaults are extremely misleading. They appear like respectable visitors, utilizing commonplace HTTP GET or POST requests. A Slowloris assault, for instance, opens a whole bunch of connections to an Apache server and sends partial HTTP requests very slowly, tying up all out there employee threads till respectable guests are locked out.
To mitigate this, you have to configure your net server (Nginx or Apache) to aggressively drop sluggish connections and rate-limit aggressive IPs.
These settings be certain that a single IP tackle can’t spam your login portal or search capabilities, whereas strict timeouts kill Slowloris connections immediately. For top-traffic functions, using UK VPS internet hosting with pre-configured Nginx proxies offers a superb baseline protection.
4. Configuring iptables for SYN Flood Safety
When you favor kernel-level filtering, iptables could be configured to drop extreme connection makes an attempt earlier than they ever attain Nginx or Apache. The restrict module is extremely efficient right here.
This rule limits new connection makes an attempt to 1 per second per IP, with a burst of three. Something exceeding this threshold is silently dropped.
5. Automating Protection with Fail2Ban
Handbook IP blocking is unsustainable throughout a reside assault. Fail2Ban dynamically reads your server logs (like Nginx entry logs or SSH auth logs) and robotically updates iptables to ban IPs exhibiting malicious conduct.
💡 Professional Tip: Fail2Ban Recidive Jail
Allow the [recidive] jail in Fail2Ban. If an attacker is repeatedly banned for brief durations (e.g., 10 minutes) throughout a number of days, the recidive jail will detect this sample and ban their IP completely (or for every week), drastically lowering background server load.
6. Conclusion & FAQ
There is no such thing as a silver bullet for DDoS mitigation. Nonetheless, by combining sysctl TCP tuning, Nginx rate-limiting, strict iptables guidelines, and automatic Fail2Ban monitoring, you create a sturdy VPS DDoS Safety structure. This multi-layered method ensures your functions stay responsive, even underneath lively duress.
Often Requested Questions
Q1: Can iptables cease a 100Gbps volumetric assault?
No. Iptables processes visitors that has already reached your server’s community card. If the incoming assault visitors exceeds your server’s bodily port pace (e.g., a 1Gbps uplink), your server will go offline. Huge volumetric assaults have to be mitigated upstream by your internet hosting supplier’s {hardware} firewalls or a CDN.
Q2: What are TCP SYN Cookies?
SYN Cookies are a way utilized by the Linux kernel to forestall SYN flood assaults. As a substitute of storing the connection request in a reminiscence queue, the server encodes the connection knowledge cryptographically within the SYN-ACK response, utterly eliminating the chance of reminiscence exhaustion.
Q3: Is Fail2Ban resource-intensive?
Fail2Ban could be very light-weight. Nonetheless, throughout an enormous Layer 7 flood, studying hundreds of log strains per second may cause excessive CPU utilization. It’s best used as a complementary software alongside Nginx fee limiting.