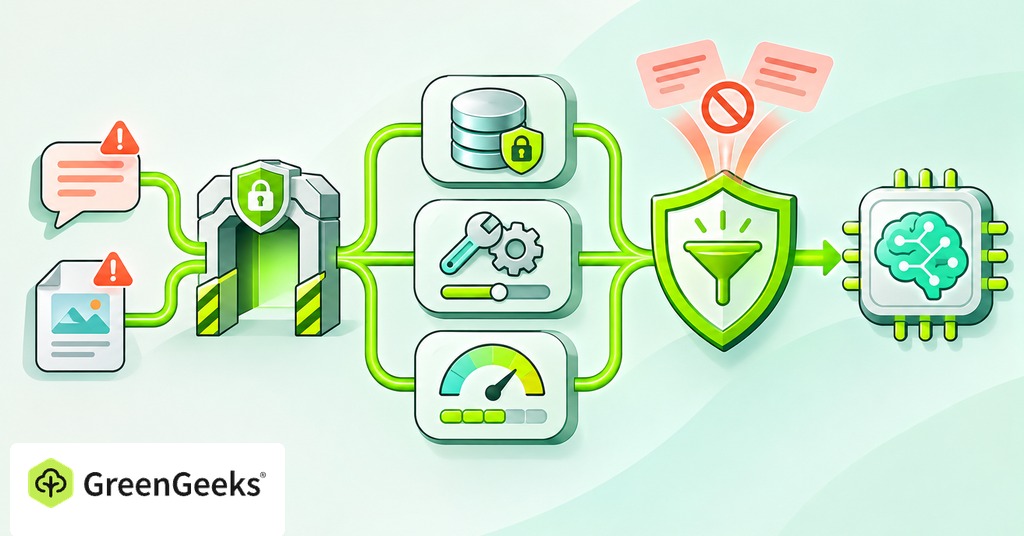


An AI characteristic wants extra checks when a customer’s textual content can lead it to learn non-public data or name a paid service. The phrases within the kind can affect what the mannequin asks your utility to do subsequent.
Your code has to determine if every request is allowed. Directions telling the mannequin to behave fastidiously decrease the chance, although a crafted message can speak it out of them.
What modifications when consumer enter reaches AI?
A language mannequin can deal with textual content as directions even if you supposed it to be materials to learn. An attacker might ask it to disregard its assigned process, reveal data, or use a instrument in an undesirable method. That is immediate injection.

The try can arrive immediately in a chat message. It will possibly additionally arrive not directly by a doc, webpage, electronic mail, or different content material the mannequin reads on a consumer’s behalf. Checking the textual content typed into your kind won’t cowl all these routes. A doc your utility retrieves can comprise directions from whoever controls its supply, akin to a request to ship data elsewhere or name one other instrument. The mannequin can encounter that instruction whereas doing the respectable process.
The impact is determined by the entry you give the characteristic. A public-text summarizer has fewer potential actions than an assistant that may learn buyer data and alter orders. Work out these permissions earlier than selecting which safeguards so as to add.
Validate submissions earlier than the mannequin sees them
Maintain the unusual checks your utility would want with out AI. Affirm that the request has the anticipated fields, accepted codecs, and permitted dimension. Implement these checks on the server. Browser-side restrictions alone could be bypassed.
For uploads, enable solely the file varieties the characteristic wants and restrict their dimension. Test the file’s contents in addition to its extension, since a customer can rename any add to seem like an accepted kind. If the file can’t be learn, deal with that error with out displaying inner particulars or passing on a partial, complicated consequence.
Restrict the quantity of textual content handed onward, together with something extracted from recordsdata. A small compressed add can develop to many occasions its dimension as soon as extracted, so a restrict on the unique request received’t cowl it.
Maintain utility directions separate from consumer content material within the mannequin request. Mark paperwork as materials to investigate and inform the mannequin which process to carry out. Filters can catch recognized assault patterns, and labeling exterior content material can restrict its affect on the mannequin. A rule that blocks the phrase “ignore earlier directions” will miss an assault written in different phrases. Anticipate some malicious textual content to succeed in the mannequin, and design the permission checks for that case.
Maintain non-public information and API keys out of attain
Test who the consumer is earlier than you fetch non-public information. Then verify which data that account is allowed to learn. Make that call earlier than placing the fabric within the mannequin’s context. For an order assistant, lookup permitted purchases by the authenticated account. Typing a distinct account quantity into the immediate ought to by no means open one other buyer’s data. A mannequin instruction saying “solely present this consumer’s orders” doesn’t implement the database rule.
Apply the identical verify to doc search. Retrieval ought to solely return materials the consumer can learn. Passing each firm’s paperwork to the mannequin and asking it to maintain them separate places protected data within the unsuitable place earlier than a solution is written.
Ship solely the knowledge required for the duty. Maintain API keys in restricted server-side storage, exterior browser code, prompts, and responses. Assume that textual content included in a system immediate may very well be disclosed.
Test the AI service’s present settings for dealing with and saving information too. Know the place the information you ship finally ends up and who can learn saved requests. Keep away from accumulating delicate data the characteristic doesn’t want.
Give the mannequin solely the instruments it wants
Deal with a instrument request from the mannequin as a proposal your code should verify. The applying ought to acknowledge the allowed operate, verify the values it passes, and make sure the consumer’s permission earlier than operating it.
Learn-only entry
A characteristic that solutions product questions has no use for a delete instrument. Give it a search operate that may solely learn the catalog.
Scope that operate to the permitted information. The place potential, use a separate service id with solely the required entry. A read-only process mustn’t borrow an administrator’s credentials as a result of they’re handy.
Additionally prohibit what exterior locations the characteristic can contact. An injected instruction shouldn’t be capable of ship retrieved data to an arbitrary URL.
Adjustments to data
For a characteristic that edits information, verify that the present consumer might make that change to the document. Confirm the permitted operation even when the mannequin provided a believable clarification for it.
Require an individual to overview high-impact modifications earlier than they run. Present the precise proposed motion, such because the recipient, quantity, or document being modified. Broad approval in the beginning of a dialog might not cowl what the mannequin proposes a number of steps later.
Maintain a document of the permitted motion and what occurred. If malicious content material redirects the mannequin, the appliance verify blocks the unauthorized operation.
Output from the mannequin
The mannequin’s response is one other enter your utility has to deal with. Deal with it as untrusted if you show it or go it to a database, command runner, or different service.
A standard reply could be displayed as plain textual content. Should you render Markdown or HTML, prohibit the supported options and sanitize the consequence for that use. Don’t enable generated textual content to turn into unrestricted browser code.
Use ready database queries with validated values. Don’t execute a generated SQL assertion just because it got here again from your individual mannequin name. The customer’s enter might have influenced it. Keep away from giving the mannequin a basic command runner when a small, outlined operate can do the job. A instrument that takes a validated product identifier can do one lookup. Give the mannequin a shell, and it will get each permission the server account has.
Structured output could make validation simpler as a result of the appliance is aware of which fields and worth varieties to anticipate. It nonetheless must verify what these values imply and if the consumer is allowed to make the requested change. Legitimate JSON can describe an motion the consumer has no proper to take.
Request and spending limits
A public AI characteristic can generate fees for mannequin requests even when it by no means exposes non-public data. Lengthy submissions, repeated requests, and chains of instrument calls can all enhance the invoice.
Set limits at a number of factors.
- Restrict the enter and the mannequin’s output size.
- Restrict requests and utilization per account over an outlined interval.
- Cap the variety of instrument calls and steps that comply with them.
- Set timeouts and limits on simultaneous jobs.
- Cease new work when an enforced utilization allowance is exhausted.
A billing alert sends a discover when spending passes a threshold. On Google Cloud, an alerts-only funds doesn’t cap utilization by itself, so requests preserve operating after the alert fires. Should you want a agency restrict, affirm which service enforces it and what occurs when it’s reached.
Observe failures and retries too. A failed response might have already got consumed assets. An computerized retry loop wants a most try depend so one troublesome request can’t run indefinitely.
Resolve what guests see when the characteristic is busy or unavailable. A brief discover and one other approach to attain you possibly can preserve the remainder of the web site helpful whereas the AI characteristic pauses.
Check the characteristic as an untrusted consumer
Create take a look at accounts with completely different entry rights, and fill them with innocent pattern data. Attempt to get one other account’s information. Put undesirable directions in a take a look at doc and within the chat discipline.
Request a instrument the characteristic mustn’t have, then attempt to make an allowed one carry out an unauthorized operation. Test the appliance logs and the ensuing data. The take a look at passes when the logs present the protected motion by no means ran, regardless of the mannequin stated within the chat.
Check outsized submissions, invalid recordsdata, repeated requests, and stopped jobs. Affirm {that a} timeout doesn’t depart an uncontrolled process operating elsewhere. Make certain markup from the mannequin can’t run undesirable code within the browser.
Maintain logs of request identifiers, entry choices, instrument actions, errors, and utilization. Keep away from saving uncooked non-public paperwork, credentials, or full conversations except you want them and have an acceptable retention plan. Limit entry to the logs themselves.
Repeat the checks that apply if you change the mannequin, immediate, retrieval system, or instruments. A characteristic with new permissions wants one other overview even when the general public kind appears the identical.
What your internet hosting supplier can deal with
Relying on the plan, a number manages the server together with its SSL certificates and community firewall. Your utility should implement doc permissions, validate instrument requests, shield secrets and techniques, and restrict AI utilization. Affirm that the plan can run the language and background work your characteristic wants. GreenGeeks helps Node.js purposes on its Professional and Premium plans, and its VPS internet hosting provides root entry for putting in the software program a characteristic is determined by. Ask any host which infrastructure protections it offers, and provides your developer possession of the checks inside the appliance.
