

What’s Managed Detection and Response (MDR) Safety?
MDR, on the earth of safety, stands for Managed Detection and Response. MDR Safety is a cybersecurity service that identifies suspicious actions and malware in your community system. It helps in detecting cyber threats that may put your confidentiality in danger. It additional eliminates these safety threats and safeguards the information.
The common time wherein threats are found within the methods is about 200 days. Nevertheless, as a result of quick tempo of MDR, these threats are recognized inside a couple of hours. It’s designed to guard the confidential particulars and information of any group that may profit its rivals.
Different instruments corresponding to CI Safety’s fast quarantine resolution has been supplied by MDR suppliers. It manages every facet of response every time any incident occurs.
Why is MDR Safety Extremely Vital?
MDR safety has grow to be important because of earn a living from home practices. Managed detection and response offers a variety of cloud administration safety for corporations that want safety providers 24/7. We’ve got listed a number of the many safety challenges because of which people can perceive the dynamics of rising safety points and the way they will put together for them.
Set up Glorious WFH (Work from Residence) Practices
Within the present world pandemic state of affairs, it is fairly wise to imagine that round 30% of the inhabitants has been working from house. So despite the fact that earn a living from home has given a number of benefits to enterprise corporations, utilizing the suitable instruments can considerably enhance their development.
Whereas working from house, workers have additionally confronted a number of threats and cyber assaults. Therefore, MDR is very important for the safety of distant endpoints that the workers entry.
Environment friendly Menace Intelligence
MDR safety can simply differentiate between actual and false threats. Organizations haven’t got to fret about false alarms. MDR has environment friendly risk intelligence because of a mixture of refined monitoring applied sciences. MDR service consists of the next applied sciences:
- Safety Data and Occasion Administration: It analyses the information for risk detection.
- Community Site visitors Evaluation: It displays the networks and analyzes the site visitors.
- Endpoint Safety Platform: It behaves as the primary line of protection and protects the platform.
- Intrusion Detection System: It scans the community for suspicious actions.
Prevention of Ransomware Assaults
Ransomware is malicious software program that may attain all through a community and expose or corrupt your information. These assaults can be made by phishing emails or hyperlinks that may hijack your information. MDR safety protects your information from the execution of ransomware assaults.
High 5 Advantages of Having MDR Safety
Here is the listing of the highest 5 advantages of getting MDR safety:
1. Dynamic Menace Panorama
Cyber threats are growing day-to-day, particularly from hijacked synthetic intelligence and Web of Issues (IoT) applied sciences. Since IoT and AI have a number of assault surfaces and haven’t got customary safety, cyber attackers can discover a option to exploit them.
To fight this, MDR safety will determine completely different threats and eradicate them by:
- Analyzing the site visitors and community system.
- Scanning the community for suspicious actions.
- Displaying rising threats that may trigger massive issues.
These rising threats can embody malware discovered within the endpoint of a system.
2. Knowledge Safety
Enterprise organizations retailer, switch, and work every day with massive quantities of various information and knowledge, and even a tiny leakage of information could cause hurt to the corporate. Additionally, this huge load of information causes difficulties with information administration and safety.
MDR safety helps in processing and managing dangers and threats throughout all of the endpoints, clouds, and entire environments.
3. Skilled Proactive Monitoring Safety Operations Heart (SOC) Analysts
MDR tightens the safety platforms for organizations. With their skilled safety operations middle (SOC) analysts, the upcoming threats are managed and eradicated shortly. These SOC analysts are educated in pc engineering, cryptography, community engineering, or pc science. They might even have credentials corresponding to CISSP or GIAC and supply 24/7 monitoring.
4. Menace Overview
A risk exercise dashboard is a necessity for any enterprise group. Such a dashboard will present full particulars about each facet of threats attacking the system. As well as, MDR safety presents border context round threats, growing the precision and accuracy of incident responses.
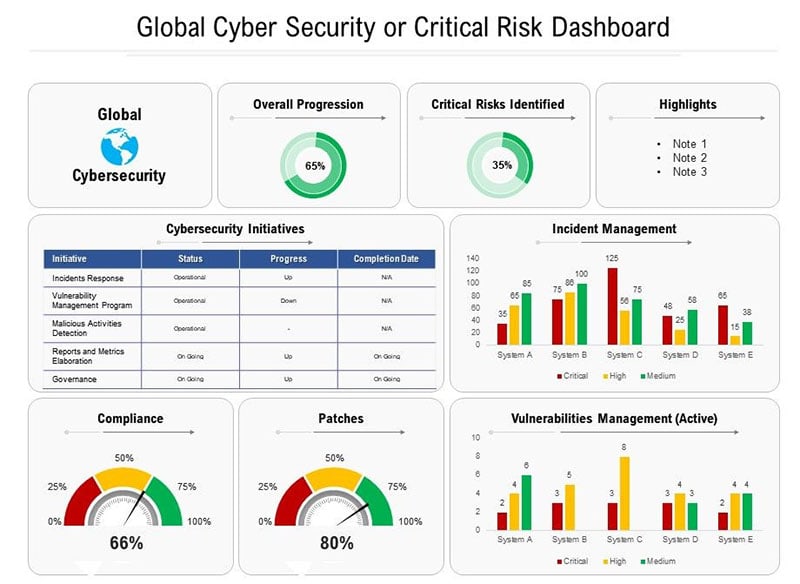
World Cyber Safety or Essential Threat Dashboard instance. Picture supply.
5. Insider Menace Administration
Most horrifying incidents happen as a result of problem of insider threats. These are threats posed by people who’ve entry to the community methods inside the group. Therefore, they will trigger much more harm than any particular person who is not linked with the group. Due to this fact, with out the administration of insider threats, organizations are susceptible.
MDR safety offers many id and entry administration options. It displays the conduct of all of the employees and workers who’ve entry to confidential information.
5 Methods Safety Points Are Solved With MDR Safety
With the newest applied sciences, cyber assaults are rising every day. Due to this fact, organizations are struggling to take care of their safety administration, so MDR has grow to be a necessity.
Listed below are the 5 methods wherein MDR solves community safety points. You may as well verify the newest safety tendencies that it’s essential to know to guard your web sites.
1. Assortment of Threats
MDR observes all site visitors flowing by means of your entire community. It makes use of safety data and occasion administration (SIEM) and intrusion detection system (IDS) instruments to gather threats. It always hunts for suspicious actions throughout all of the site visitors coming by means of.
With the assistance of real-time monitoring and correlation, it detects all identified and unknown threats. Unknown threats are malicious codes which might be uncommon and have by no means been seen earlier than, additional lowering the typical time wanted to determine threats, so as to react shortly to several types of cyber assaults.
2. Identification of Threats
Unprotected software program and methods are one of the best treats for hackers. With the assistance of MDR, common scans verify for vulnerabilities inside lively networks. It additionally identifies the weak factors within the system and can spotlight them, minimizing the possibilities of exploitation.
3. Analyzation of Threats
MDR makes use of forensic evaluation to disclose any malware exercise within the system. It additionally examines and analyzes the information so as to determine an upcoming assault or suspicious sample. Additional, it tightens the safety of information and scrutinizes information for varied classes of threats.
4. Response
When any risk is detected, MDR safety performs an evaluation. Alert notifications are then despatched to the officers and the SOC analysts. It offers the SOC workforce the prospect to behave quickly and deal with the state of affairs nicely. The foundation reason for the breach is then found, and the risk is eradicated earlier than it may hurt the information and information.
5. Compliance
MDR can produce precise compliance experiences for an intensive vary of compliance requirements corresponding to PCI, HIPAA, NERC, CIP, SOX, GDPR, and far more. It detects the potential breaches early in order that they are often addressed. MDR collects log and occasion information from throughout the group and presents it in an easy-to-read doc.
Why Select Alert Logic and Liquid Net
At Liquid Net, we all know that our prospects wish to have safe internet hosting providers, which is why we teamed up with Alert Logic.
Alert Logic Safety & Compliance Suite is an inclusive, end-to-end safety and compliance resolution that may present particulars about risk detection and scan your entire community for any safety risk. It consists of real-time reporting, 24/7 monitoring, and remediation administration. It would additionally assist in lowering the dangers of cyber assaults to your corporation with tight safety.