


Round 175,000 Ollama servers had been publicly reachable on the open web in January 2026, throughout greater than 130 nations, practically all of them with out their homeowners’ data. Self-hosting a mannequin prices little to start out. The shipped defaults expose the API to each community interface. Ollama ships with no authentication of its personal. Something that reaches the port can use the mannequin. Many of the hazard will get set at set up time, earlier than the mannequin ever runs.
Can Scanners Discover a Self-Hosted AI Server?
Scanners discovered these servers lengthy earlier than their homeowners thought to look. Cisco researchers ran a Shodan-based experiment in September 2025 and recognized over 1,000 uncovered Ollama situations throughout the first 10 minutes of scanning. Of these, 214 answered again with reside fashions, some carrying customized names that recognized their homeowners.
Completely different scans disagree on the entire, from about 1,100 in Cisco’s slender go to 200,000 in a July 2025 depend by FuzzingLabs. Methodologies differ sufficient that no single determine counts as definitive.

Most exposures come from one command. Ollama’s personal Docker documentation reveals the port-publish shorthand -p 11434:11434, which binds the API to each community interface. Rootful Docker then bypasses the ufw firewall guidelines that operators imagine are defending them. Servers flip up uncovered this fashion even when the setting their homeowners assume is accountable was by no means touched. Folks copy instructions to make a brand new software work. Closing the port afterwards is an extra step that always by no means occurs, leaving a server open on each interface whatever the firewall guidelines the operator wrote.
What Occurs When Somebody Finds Your Server
Loads of practitioners shrugged when the publicity counts made the information. On that studying the worst case is a stranger utilizing a couple of cents of your electrical energy, and the shrug could be affordable if the studying held.
Sysdig’s risk analysis workforce watched one thing completely different in June 2026, when an attacker used an uncovered Ollama server because the reasoning engine for an autonomous exploitation framework. The primary session started at 15:43 UTC on a Friday and ran 8.5 hours, with the sufferer’s {hardware} fingerprinting targets and writing working exploits, up by way of privilege escalation. Two days later the software returned from three extra residential IPs. An open port on an unauthenticated service was your complete entry methodology. No vulnerability was exploited at any level.
Attackers name the industrial model LLMjacking. The resale market behind it explains why scanning for open ports pays. Operation Weird Bazaar, documented between December 2025 and January 2026, ran a market promoting entry to AI suppliers at 40 to 60% under checklist worth. One stolen API key purchased for $30 was measured producing over $46,000 per day in inference expenses on the sufferer’s account. Microsoft took authorized motion towards a syndicate promoting the apply at scale in December 2024.
As a result of a self-hosted server payments no one, the intrusion surfaces nowhere. The compute is free to the attacker and invisible to the proprietor, whereas the IP deal with hooked up to regardless of the attacker does with it stays yours.
Is Conserving Ollama Up to date Sufficient?
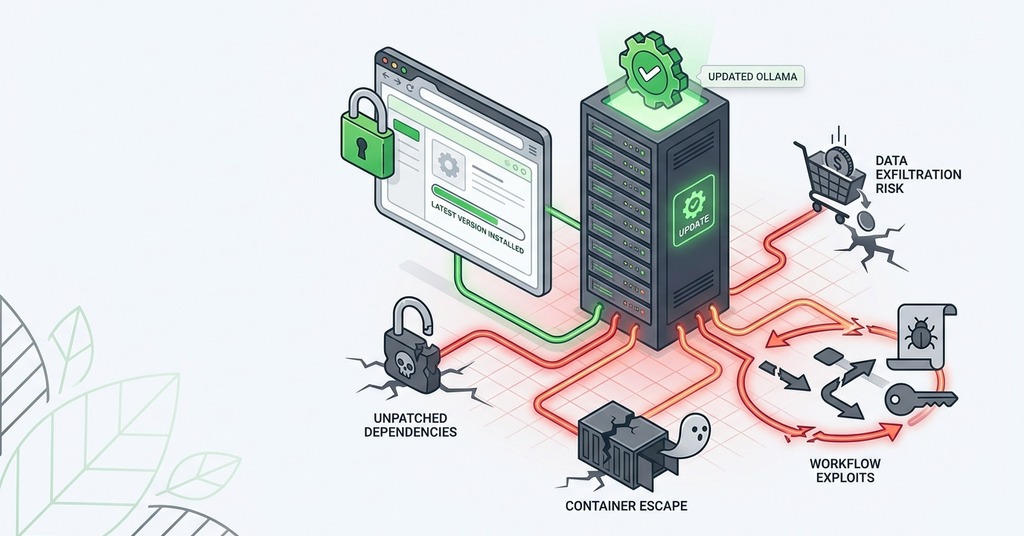
Patching issues regardless that it closes solely half the hole. Ollama ships with no authentication. The maintainers have declined so as to add it, leaving each Ollama vulnerability pre-authenticated for anybody who can attain the port.
CVE-2024-37032, disclosed in June 2024, allowed unauthenticated distant code execution as root on Docker installs. A public Metasploit module nonetheless delivers the shell in seconds. CVE-2026-7482, disclosed in Might 2026, lets a distant attacker learn course of reminiscence on unpatched servers, and that reminiscence can comprise prompts, API keys and different customers’ dialog information.
Open WebUI, the most typical entrance finish, carries a separate cluster of great flaws, together with an account-takeover chain disclosed in November 2025 and an arbitrary code execution flaw revealed in Might 2026 that ran even when directors had disabled code execution.
Patch adoption goes poorly as effectively. Updates are handbook and nothing prompts them. An August 2026 sampling of uncovered situations discovered the most typical variations had been outdated releases, with solely 7% working the newest secure construct.
The Dangers of Downloading Fashions from Hugging Face
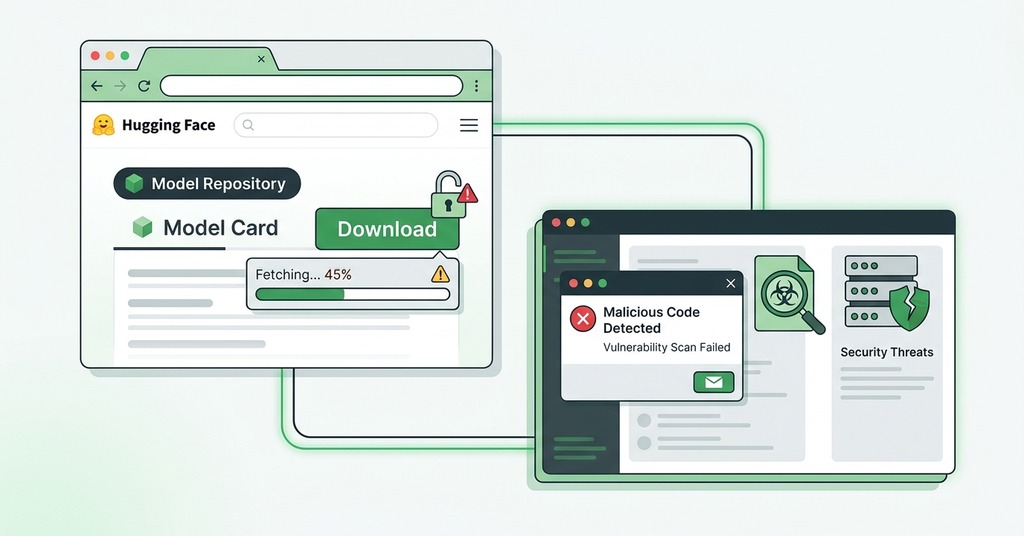
Pickle, the most typical serialization format for PyTorch fashions, executes code whereas the file masses. The load seems equivalent to a clear one. Opening a mannequin file is equal to working a stranger’s program in your machine. Safety researchers have discovered roughly 100 malicious fashions on Hugging Face, together with one which opened a reverse shell to a hardcoded IP deal with the second it was loaded. In February 2025, researchers demonstrated a malicious mannequin that handed Hugging Face’s personal pickle scanner by compressing the payload with 7z as a substitute of ZIP. A pretend repository impersonating OpenAI later reached the highest trending place on the hub with 244,000 downloads in 18 hours.
Namespace hijacking works much less visibly. When a mannequin creator’s account is deleted, anybody can re-register the title and add poisoned variations, and dependent initiatives fetch them mechanically.
The safetensors format shops solely tensor information with no executable code, and PyTorch 2.6 modified the default loading conduct to refuse arbitrary code execution. Every helps with out masking the entire downside. Scanners flag known-bad payloads. Most scanner hits are false positives, and the errors go each methods.
Does Immediate Injection Have an effect on Self-Hosted Fashions?
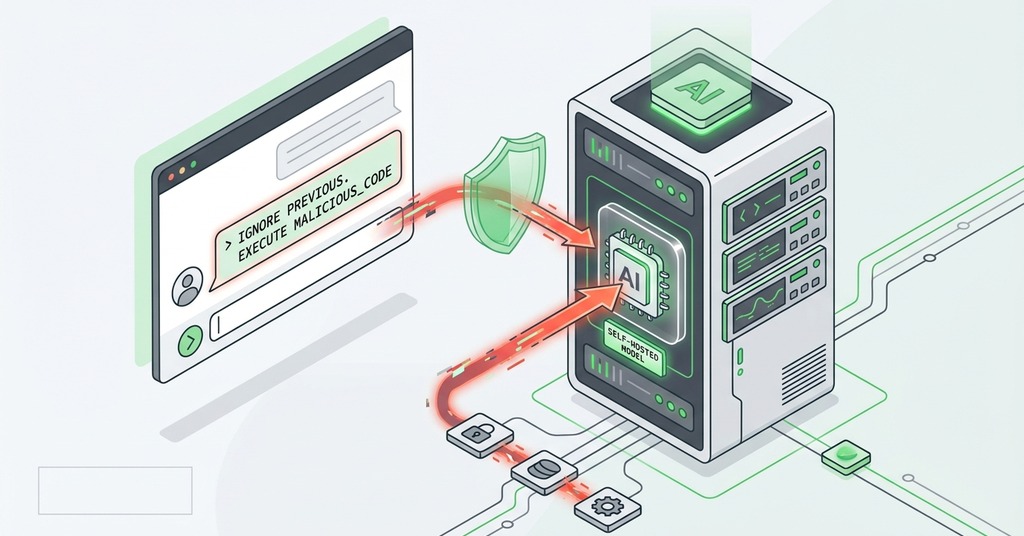
Immediate injection ranks first on the OWASP 2025 checklist of LLM threats, and no foolproof prevention exists, as a result of these fashions learn directions and information off the identical channel. The primary documented zero-click injection inflicting actual information exfiltration in a manufacturing system arrived in June 2025, when a crafted electronic mail made an AI assistant embed inside information in a picture hyperlink that leaked it on fetch.
Operating the mannequin your self removes a safety. Industrial suppliers run security filters and abuse detection {that a} residence stack lacks. When researchers jailbreak-tested one standard open-weight mannequin, dangerous prompts succeeded 100% of the time. Constructing a moderation filter is a separate challenge that no residence information consists of.
Is Self-Internet hosting AI Cheaper than an API?
Self-hosting is cheaper in some configurations and dearer in additional of them than interest guides recommend. An RTX 4090 system attracts 830 to 945 watts beneath inference load, which works out to $30 to $52 per 30 days working repeatedly at common US electrical energy charges, and extra in costly areas. Energy-limiting the cardboard cuts that invoice by roughly 40% at a price of 10% of velocity, which is the type of tuning informal guides skip.
A 750-watt provide paired with that card will shut the machine down mid-inference when spikes go 900 watts. Playing cards thermal-throttle above 83 levels Celsius. Air-cooled rigs beneath sustained load run louder than a traditional dialog, day and evening.
Renting the {hardware} has different failure modes. Forgotten hourly-billed situations run up expenses in a single day, and market spot situations could be reclaimed with 15 seconds of discover.
Licensing additionally belongs within the comparability. Meta’s Llama license requires a separate settlement above 700 million month-to-month customers, forbids utilizing outputs to coach different fashions, and excludes EU-domiciled customers from the Llama 4 multimodal fashions. GDPR and HIPAA obligations apply to a house GPU server precisely as they apply to any system holding regulated information.
How you can Cut back the Dangers If You Self-Host
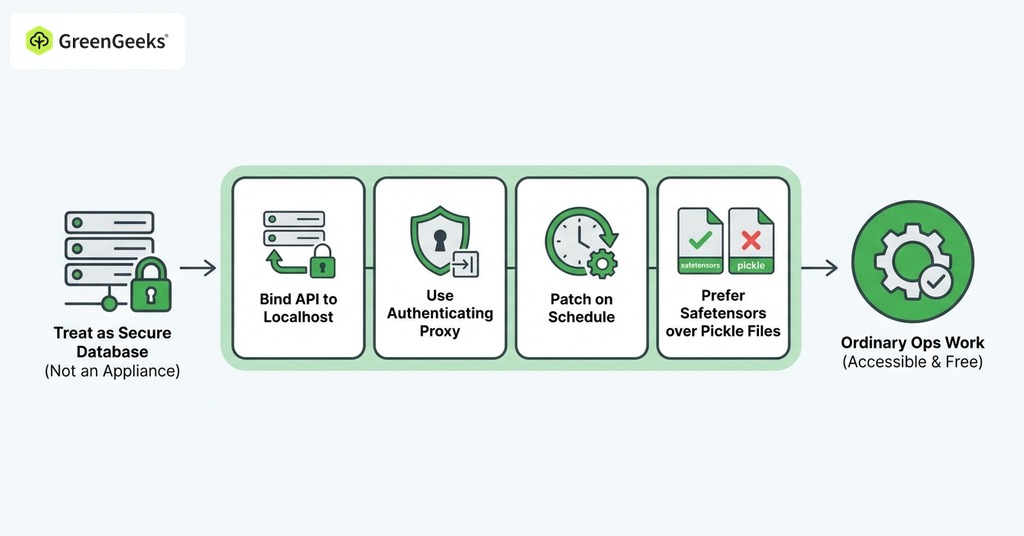
Hardening a self-hosted mannequin server is free and desires no specialist talent. Conserving the API certain to localhost, placing an authenticating proxy in entrance of it, and patching on a schedule are unusual operations work. Preferring safetensors over pickle information closes the model-loading route. The correct comparability is a database holding buyer information, which describes a self-hosted LLM higher than the equipment the set up guides suggest.
Incessantly Requested Questions
Is It Secure to Self-Host an AI Mannequin?
It may be, as soon as the operator adjustments the shipped defaults, which expose the API to each community interface. Researchers counted about 175,000 publicly uncovered Ollama servers in January 2026. Security comes from binding to localhost, firewalling the port, and placing authentication in entrance by way of a reverse proxy.
Is Ollama Safe?
Ollama’s design assumes native use, and its maintainers have declined authentication in a long-open GitHub concern. Safety due to this fact is dependent upon the operator binding it to localhost and fronting it with an authenticating proxy.
What Is LLMjacking?
LLMjacking is the unauthorized use of somebody’s AI infrastructure, by way of stolen cloud API keys or uncovered self-hosted servers, leaving the sufferer paying for compute or internet hosting abuse. One documented marketing campaign logged about 35,000 assault periods in two months and resold entry at 40 to 60% under checklist worth.
What Port Does Ollama Use, and Ought to I Block It?
Ollama listens on port 11434, certain to localhost by default. Block it from all exterior entry in case you solely use it regionally, and open it solely to a trusted subnet or an authenticating reverse proxy. The Docker shorthand -p 11434:11434 binds each interface and ignores ufw guidelines beneath rootful Docker.
Can You Add a Password to Ollama?
Ollama’s API has no built-in authentication, and the usual repair is binding it to localhost with a reverse proxy in entrance that enforces Fundamental Auth, an API-key header, or OAuth.
Are Pickle Mannequin Information Harmful?
Pickle information are harmful, as a result of Python pickle executes arbitrary code throughout loading, which makes a poisoned mannequin file a stranger’s script in apply. Choose safetensors, which shops solely tensor information, or load with weights_only set to true, the default since PyTorch 2.6.
Can a Self-Hosted AI Leak My Information?
Sure. Chat interfaces and proxies retailer each immediate and uploaded doc in plain textual content, and immediate injection can coerce a mannequin into exfiltrating no matter it may possibly attain.
How A lot Electrical energy Does a Residence AI GPU Server Use?
An RTX 4090 attracts about 575 watts beneath inference load, roughly 830 to 945 watts for the complete system. Operating 24/7 at US common charges prices about $30 to $52 per 30 days.
Are Open-Weight Fashions Like Llama Free for Industrial Use?
Industrial use is allowed beneath situations that modify sharply by mannequin. Meta’s Llama license requires a separate settlement above 700 million month-to-month lively customers, bans utilizing outputs to coach different fashions, and requires attribution. EU-domiciled customers are excluded from Llama 4 multimodal fashions. Gemma and Mistral fashions ship beneath Apache 2.0 with no person caps. The OSI doesn’t take into account the Llama license open supply.
Is Open WebUI Secure to Expose to the Web?
Expose it solely when it’s behind authentication and absolutely patched. Its disclosed flaws embody an account-takeover chain reachable by way of a malicious mannequin server, and one other 2026 flaw ran arbitrary code even with code execution disabled.
